Release notes
A management console. The default engine stays KiviDB 1.1.2.
0.6.0
A management console. The default engine stays KiviDB 1.1.2.
Read before upgrading: with console authentication on, the console now has
its own sign-in page and session cookie in place of the browser's Basic-auth
box. Scripts that call its API with Basic auth (curl -u) keep working.
Compatibility
| Requires or ships | Version |
|---|---|
| Kubernetes | 1.27 or later |
| Helm | 3.9 or later |
| Default engine | docker.io/kividb/kividb:v1.1.2 (and the -tls, -lua, -full variants) |
| Images | docker.io/kividb/kividb-operator:0.6.0, kividb-operator-agent:0.6.0, kividb-operator-gui:0.6.0; the same tags on ghcr.io/kividbio/ |
| Helm chart | oci://registry-1.docker.io/kividb/kividb-operator-chart or oci://ghcr.io/kividbio/kividb-operator-chart, version 0.6.0, signed with cosign |
| CRD API version | kividb.io/v1alpha1 (unchanged) |
Added
- A sign-in page (
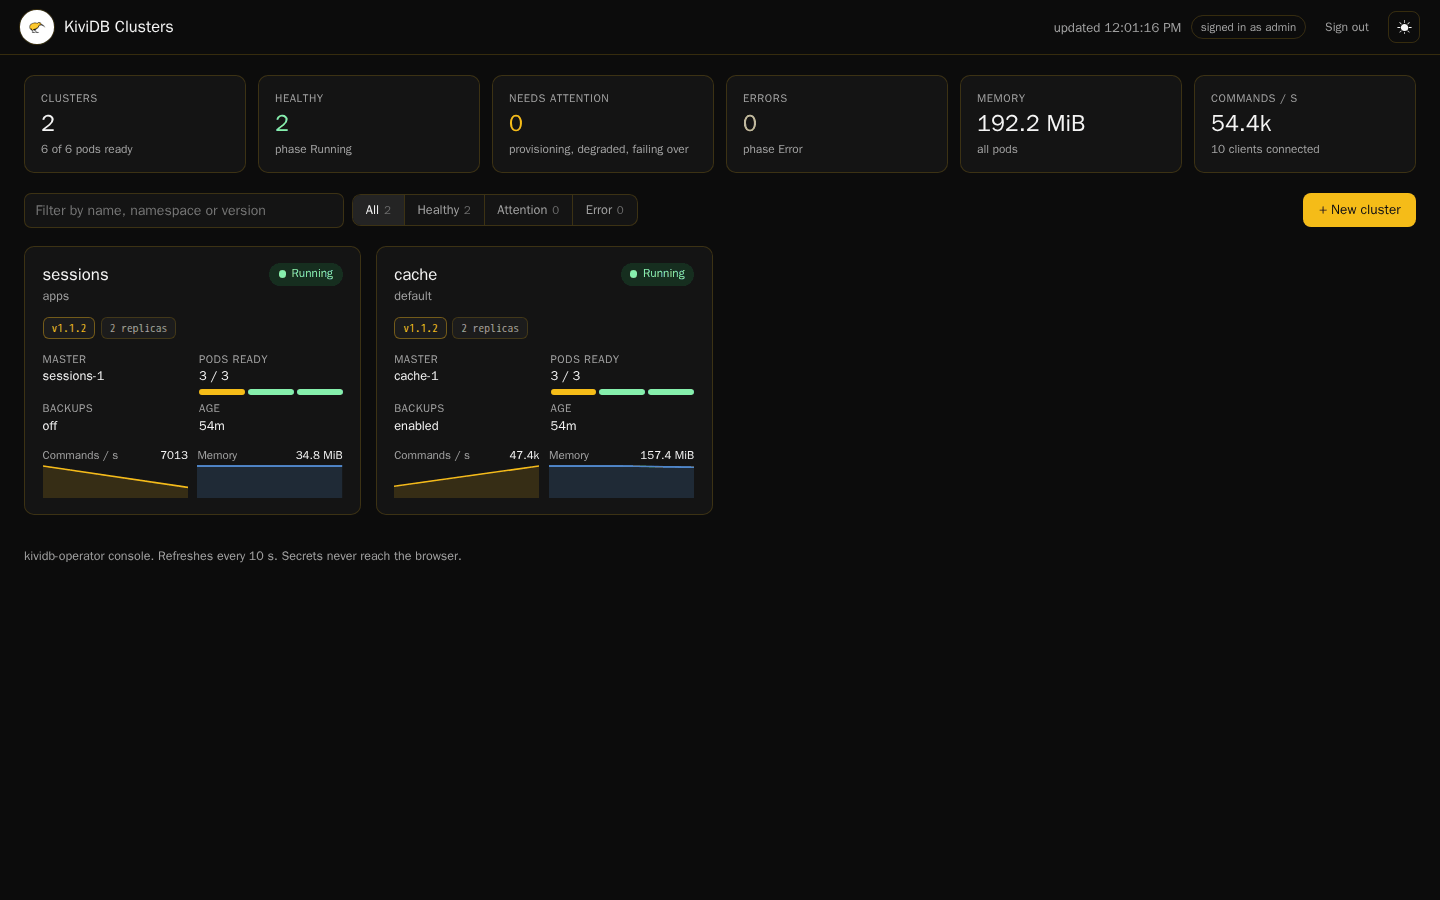
/login). Signing in sets a session cookie (HttpOnly, SameSite=Lax, Secure over HTTPS, 12 hours) signed with a random key made when the console starts, so nothing in it comes from the password and a restart (which changing the password needs) ends every session. Ten failed attempts from one address lock it out for five minutes. Sign out is in the top bar. - Dashboard. Totals for clusters (healthy, needing attention, in error), memory, commands per second and clients across all pods; a search box and a health filter; and for each cluster its engine version and build, a pod bar, and sparklines of the last hour's commands per second and memory.
- Topology on a cluster's page: the master and its replicas, each with its readiness, memory, keys, replication offset and node, and how far each replica is behind the master.
- Charts with axes, a hover readout of every pod, a legend and a 1 h / 6 h / 24 h range: commands per second, memory and clients per pod, and each replica's replication lag.
- New cluster (
/new): a form for the name, namespace, build (standard, lua, tls, full), replicas, storage, memory and CPU, storage class, master service type, backups and monitoring. The manifest beside it is the API server's dry run of the form, updated as you type, and can be copied forkubectl apply. Creating needs a login, as every other change does. - Light and dark themes, following the system setting until you pick one, and a layout for phones and tablets.
- Logs with a line count, follow mode and errors and warnings in colour;
the console prints replies as
redis-clidoes, takes quoted arguments and keeps a history on the arrow keys. - On a read-only console, every button that would only be refused is disabled and says why.
Changed
- Confirmations are in-page dialogs; deleting a cluster asks for its name.
- A cluster's tabs are Overview, Metrics, Logs, Console, Backups, and Events & operations.
- The console's ClusterRole adds
createonkividbclustersandget/listonstorageclasses, for the new-cluster form. - Default agent image
docker.io/kividb/kividb-operator-agent:0.6.0. A cluster that leavesspec.agentImageunset rolls its pods to it, one by one, when the operator is upgraded. - The chart is signed with cosign, and its Artifact Hub metadata is published with it.
0.5.2
A security release. The default engine stays KiviDB 1.1.2.
Security
github.com/klauspost/compress1.17.9 to 1.18.7 (CVE-2026-63209, GHSA-259r-337f-4rfw), which reaches the agent through the S3 client it uses for backups. govulncheck finds no call to the vulnerable code.golang.org/x/net0.56.0 to 0.60.0 andgolang.org/x/crypto0.53.0 to 0.57.0, fixing the advisories govulncheck reports for them; none of the vulnerable code is called either.
Changed
- Built with Go 1.26; building the operator from source needs it.
- Default agent image
docker.io/kividb/kividb-operator-agent:0.5.2, rolled to clusters that leavespec.agentImageunset, one pod at a time.
0.5.1
The default engine is KiviDB 1.1.2, which fixes a RESTORE that could crash
the server and expired keys piling up under a steady load of writes with a TTL.
Validated on Azure Kubernetes Service (three nodes): the standard, TLS, Lua and
full builds, a master killed under write load, snapshot chaos, a failover and a
restore, backup to S3 and restore, and in-place upgrades from KiviDB 1.1.0 to
1.1.2 under write load. No acknowledged write was lost in any of them.
Changed
- Default engine
docker.io/kividb/kividb:v1.1.2(it was v1.1.0). A cluster that leavesspec.imageunset is upgraded to 1.1.2 when the operator is upgraded, its pods rolled one by one. Setspec.imageto stay on a version. KiviDB's image has no shell from 1.1.2; the operator only talks to it over RESP through its agent, so nothing changes for it. - Default agent image
docker.io/kividb/kividb-operator-agent:0.5.1.
Fixed
- The docs named the backup CronJob
<cluster>-snapshot; it is<cluster>-backup.
0.5.0
Validated on Azure Kubernetes Service (three nodes) against KiviDB v1.1.0: a cluster without a password, a password-protected cluster with ACL users upgraded in place from v1.0.5 to v1.1.0 under write load, a master killed under write load, and the TLS build with a client CA. No acknowledged write was lost in any of them.
Compatibility
| Requires or ships | Version |
|---|---|
| Kubernetes | 1.27 or later |
| Helm | 3.9 or later |
| Default engine | docker.io/kividb/kividb:v1.1.0 (and the -tls, -lua, -full variants) |
| Images | docker.io/kividb/kividb-operator:0.5.0, kividb-operator-agent:0.5.0, kividb-operator-gui:0.5.0; the same tags on ghcr.io/kividbio/ |
| Helm chart | oci://registry-1.docker.io/kividb/kividb-operator-chart or oci://ghcr.io/kividbio/kividb-operator-chart, version 0.5.0 |
| CRD API version | kividb.io/v1alpha1 (unchanged) |
Changed
- Default engine
docker.io/kividb/kividb:v1.1.0. Images now come from Docker Hub (docker.io/kividb/...) and GHCR (ghcr.io/kividbio/...), with the same tags in both. The operator, agent and GUI images, the chart, the CRD defaults, the samples and the docs point at Docker Hub. - Default agent image
docker.io/kividb/kividb-operator-agent:0.5.0. - The release attaches the CRDs as well as the packaged chart.
Fixed
- A cluster without a password served nobody on KiviDB v1.1.0. KiviDB
1.1.0 enforces protected mode: with no password on the
defaultuser and nobind, it refuses every client that is not on the pod's loopback, the other pods' replication included. The agent, on loopback, still reported the pods healthy, so such a cluster showedRunningwhile every client and replica gotDENIED. The operator now setsbind 0.0.0.0, the address KiviDB always listened on, unless you configurebindorprotected-modeyourself. Existing clusters are rolled onto the new configuration by the operator upgrade. - The chart's
agent.imagewas not used. Every cluster withoutspec.agentImagepulled the image built into the operator, so mirroring the images to a private registry through the chart values left the sidecars unpullable. The chart now passesagent.imageto the manager's new--default-agent-imageflag. - The TLS port was on no Service. The pods listened on it, but the master,
replica and headless Services carried only the KiviDB and agent ports, so TLS
clients could reach KiviDB only by pod IP. With TLS on, all three now carry
it, named
tls.
Upgrade notes
- KiviDB v1.1.0 with a TLS CA requires client certificates. With
tls.certSecretRef.caKeyset, a TLS client without a certificate signed by that CA is refused; earlier engines let it in. Add the directivetls-auth-clients: optional(or"no") to keep accepting it. - Upgrade the operator first (its CRDs and its chart; see
Upgrade the operator), then
change
spec.image: the operator rolls the pods replicas first, then fails the master over, as for any engine upgrade.
Earlier releases
The notes for 0.4.0 and earlier are on GitHub.